 Facebook
 Google
 GitHub
 Linkedin

Hello,
I am trying to reverse-engineer a closed, proprietary RS485 protocol used by a Spagnol agricultural irrigation controller. My objective is to replace an existing 1.2 km RS485 cable connection with a wireless communication link.
1. Hardware and Setup
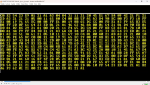
My current SBUS capture is unreadable, and I suspect a baud rate mismatch.
Here are my observations:
Based on my calculations using FCY = 4 MHz, the possible baud rates appear to be 9600, 19200, or 38400 baud. However, I have not yet determined the correct rate.
3. Questions and Help Needed
Question 1 – Automatic Baud Rate Detection
Is there any free software that can automatically detect an unknown UART baud rate or measure the shortest bit duration on an RS485 line?
I know that a logic analyser combined with PulseView/sigrok can perform this analysis. However, is there a software-only solution that works with a standard USB-to-RS485 adapter?
Question 2 – Unknown Binary Protocol Analysis
Is there a sniffer or protocol analysis tool capable of handling an unknown binary protocol, including:
Question 3 – Checksum and CRC Identification
Has anyone successfully reverse-engineered a similar proprietary industrial communication protocol?
I would particularly appreciate advice on methods or tools for identifying unknown checksum algorithms, including CRC variants, XOR checksums, or other integrity mechanisms.
4. Expected Result
My goal is to obtain a reliable understanding of the communication protocol, decode the frames correctly, and eventually implement a wireless communication bridge without modifying the original irrigation controller.
Any recommendations, tools, practical experience, or technical documentation would be greatly appreciated.
Thank you for your help.
Khalid
I am trying to reverse-engineer a closed, proprietary RS485 protocol used by a Spagnol agricultural irrigation controller. My objective is to replace an existing 1.2 km RS485 cable connection with a wireless communication link.
1. Hardware and Setup
- Controller: Spagnol agricultural irrigation controller.
- RS485 transceiver: ADM3485.
- Capture hardware: USB-to-RS485 adapter.
- Capture software: RealTerm (HEX mode).
My current SBUS capture is unreadable, and I suspect a baud rate mismatch.
Here are my observations:
- The same 5-byte header (66 78 66 00 E6) appears at the beginning of every frame.
- Two different frame types seem to alternate, each approximately 34 bytes long, possibly corresponding to a master poll and slave response.
- The captured data is dominated by bytes such as FE, 66, 78, and E6.
- Bit 0 of almost every decoded byte appears to match the UART start bit.
- When analysing the bitstream, signal transitions appear to last an even number of bit-times, mostly 2, 4, or 8.
Based on my calculations using FCY = 4 MHz, the possible baud rates appear to be 9600, 19200, or 38400 baud. However, I have not yet determined the correct rate.
3. Questions and Help Needed
Question 1 – Automatic Baud Rate Detection
Is there any free software that can automatically detect an unknown UART baud rate or measure the shortest bit duration on an RS485 line?
I know that a logic analyser combined with PulseView/sigrok can perform this analysis. However, is there a software-only solution that works with a standard USB-to-RS485 adapter?
Question 2 – Unknown Binary Protocol Analysis
Is there a sniffer or protocol analysis tool capable of handling an unknown binary protocol, including:
- Automatic frame detection based on idle gaps.
- Binary frame splitting and comparison.
- Checksum or CRC identification.
- Analysis of unknown frame structures.
Question 3 – Checksum and CRC Identification
Has anyone successfully reverse-engineered a similar proprietary industrial communication protocol?
I would particularly appreciate advice on methods or tools for identifying unknown checksum algorithms, including CRC variants, XOR checksums, or other integrity mechanisms.
4. Expected Result
My goal is to obtain a reliable understanding of the communication protocol, decode the frames correctly, and eventually implement a wireless communication bridge without modifying the original irrigation controller.
Any recommendations, tools, practical experience, or technical documentation would be greatly appreciated.
Thank you for your help.
Khalid
Attachments
-
 269.6 KB Views: 1
-
 1.9 MB Views: 2